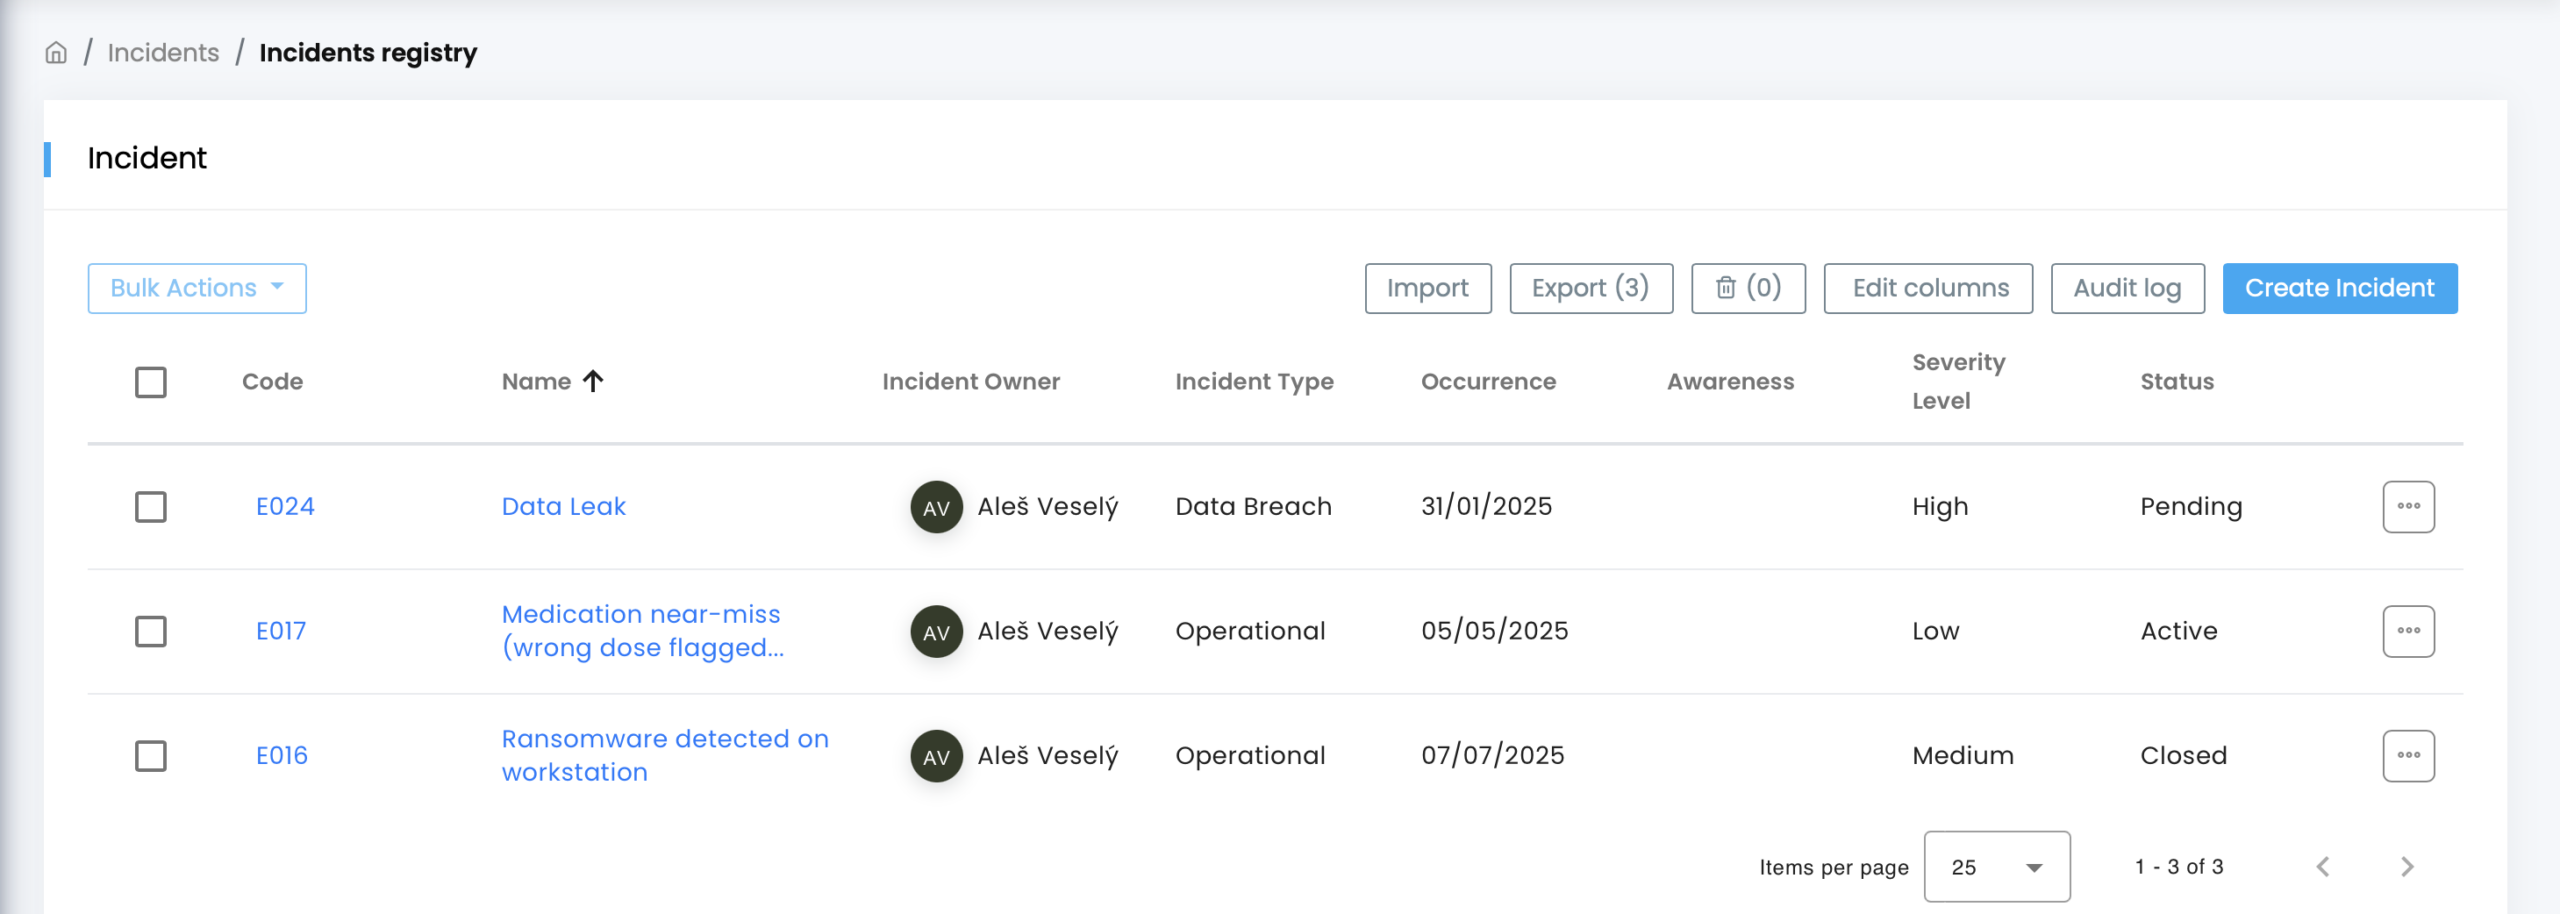
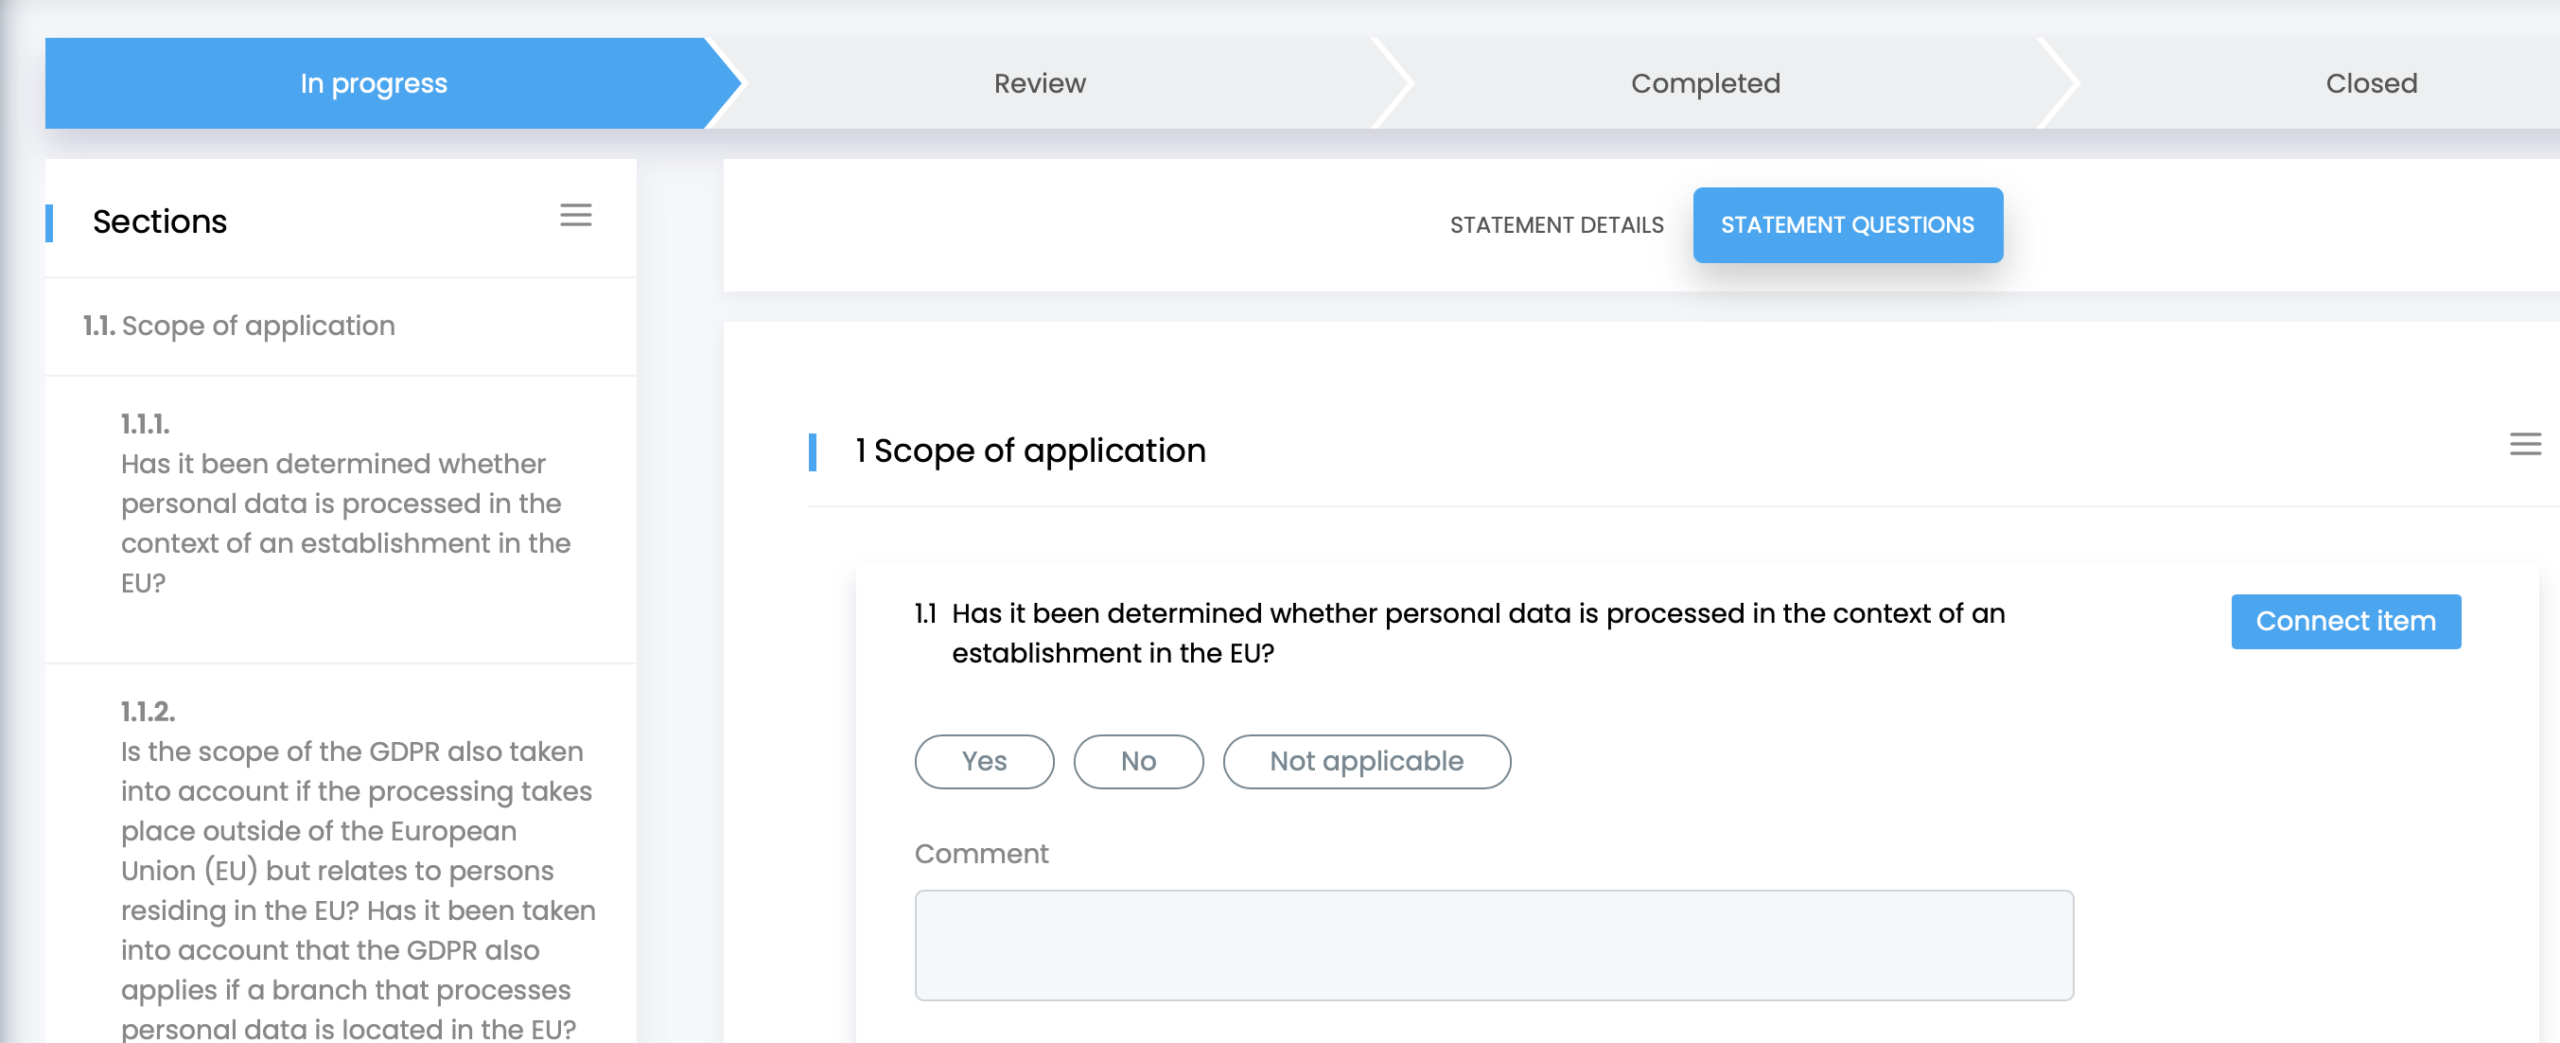
Keep your Record of Processing Activities (ROPA) under control and manage Data Protection Impact Assessments (DPIAs) for each process efficiently and in an auditable way. Map the data breach incidents in your Incident Register (see the next tab).
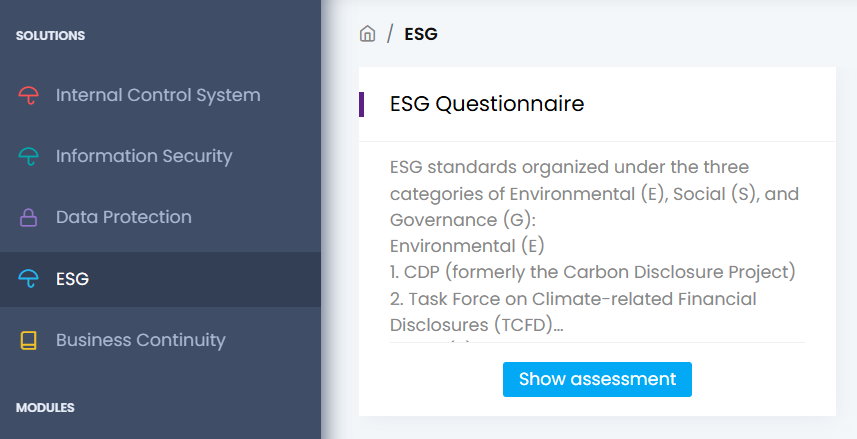
Maintain a centralised register of ESG requirements, objectives, metrics, actions, and evidence. Track sustainability performance, map information to frameworks such as CSRD and ESRS, and monitor progress against targets. Gain control over ESG ownership, reviews, and reporting through a structured and auditable workflow.
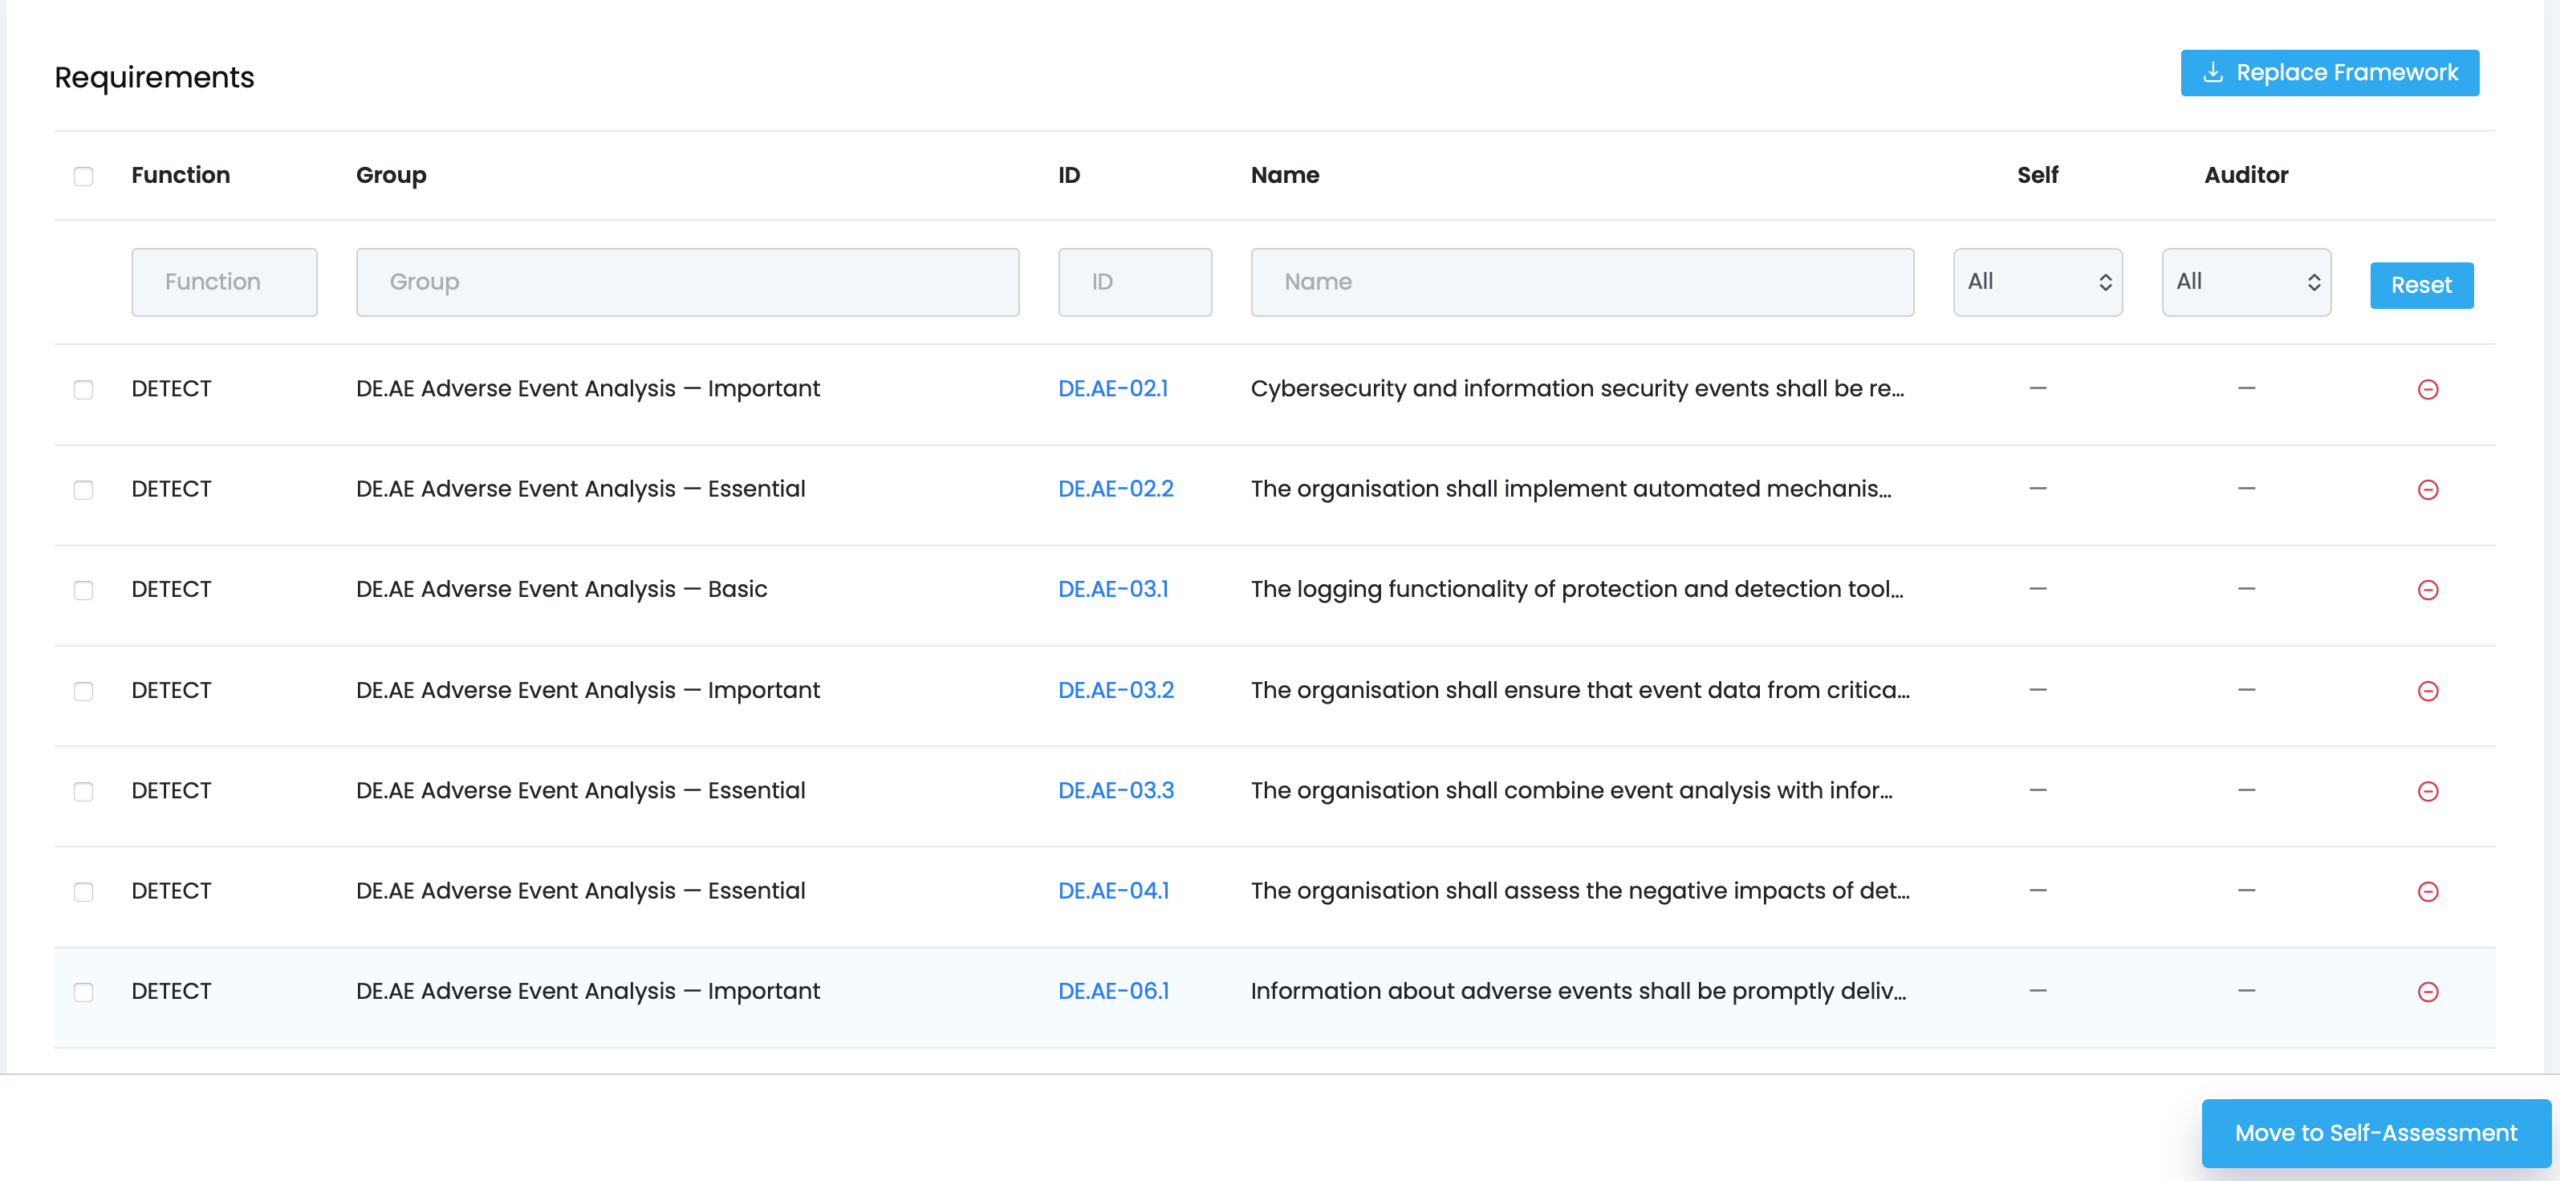
Implement Cyber Fundamentals via an intuitive GRC tool. Achieve and maintain Cyber Fundamentals compliance by tracking the controls and requirements associated with your organisation's Basic, Important, or Essential category.
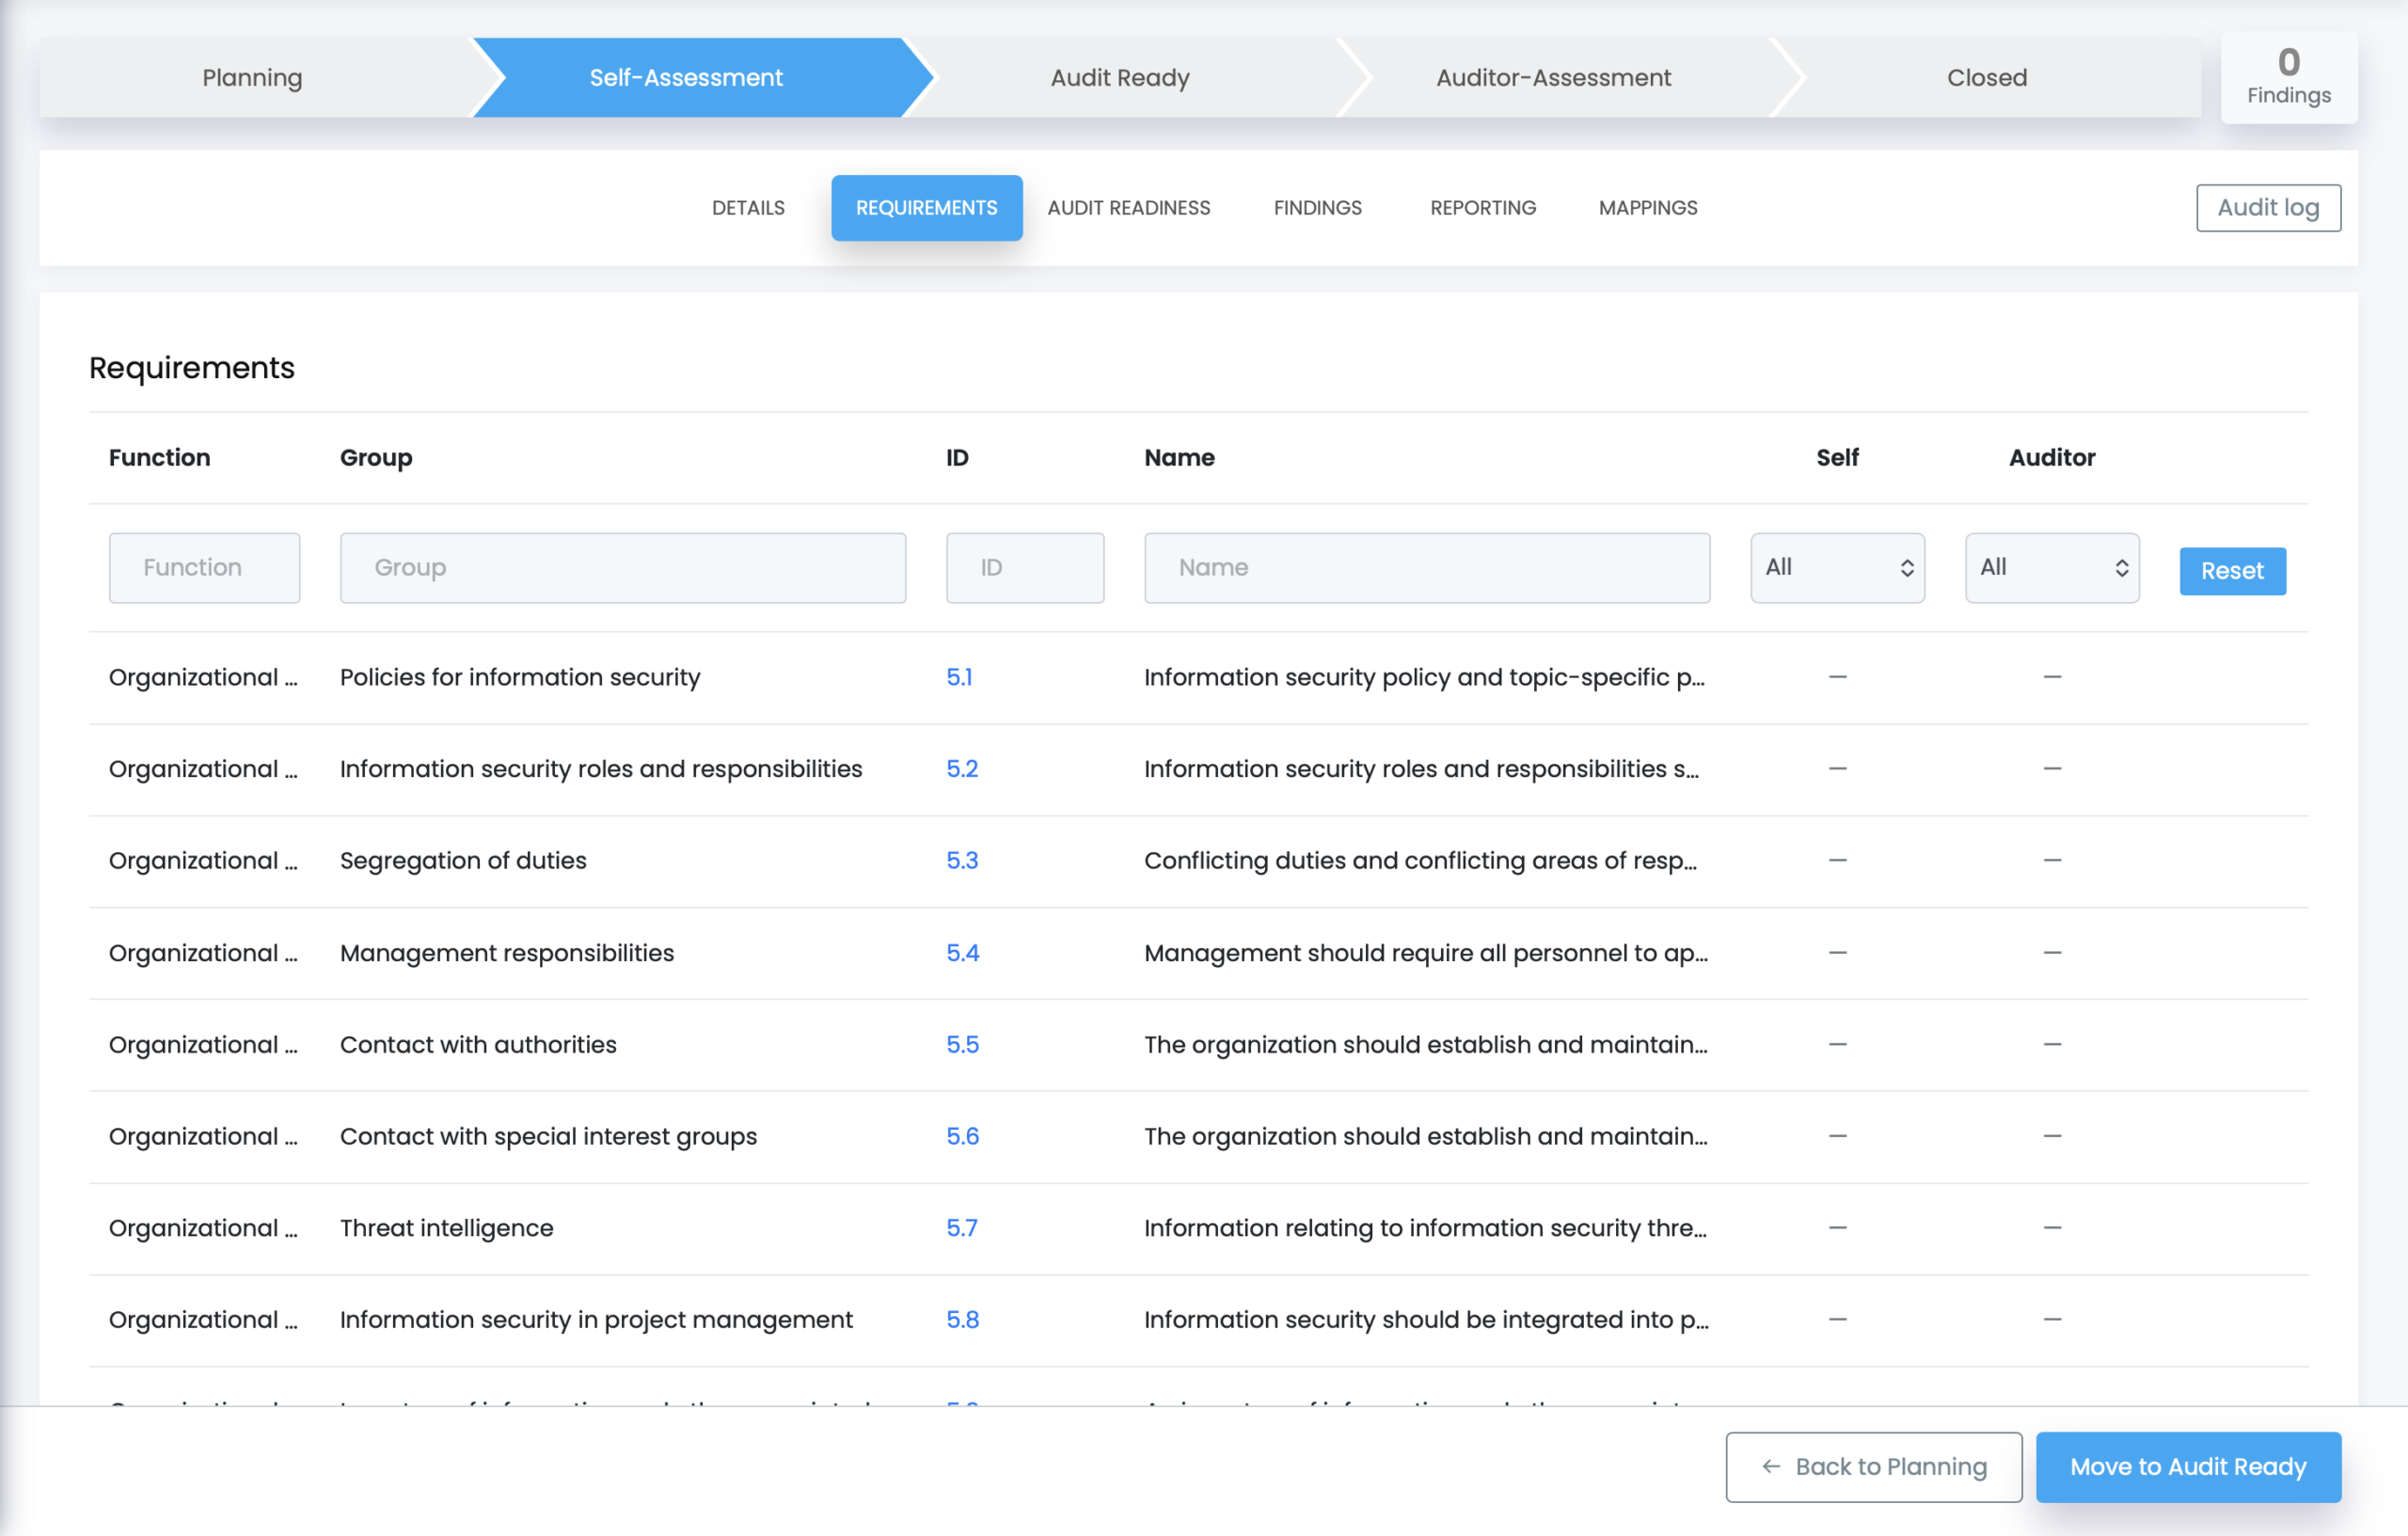
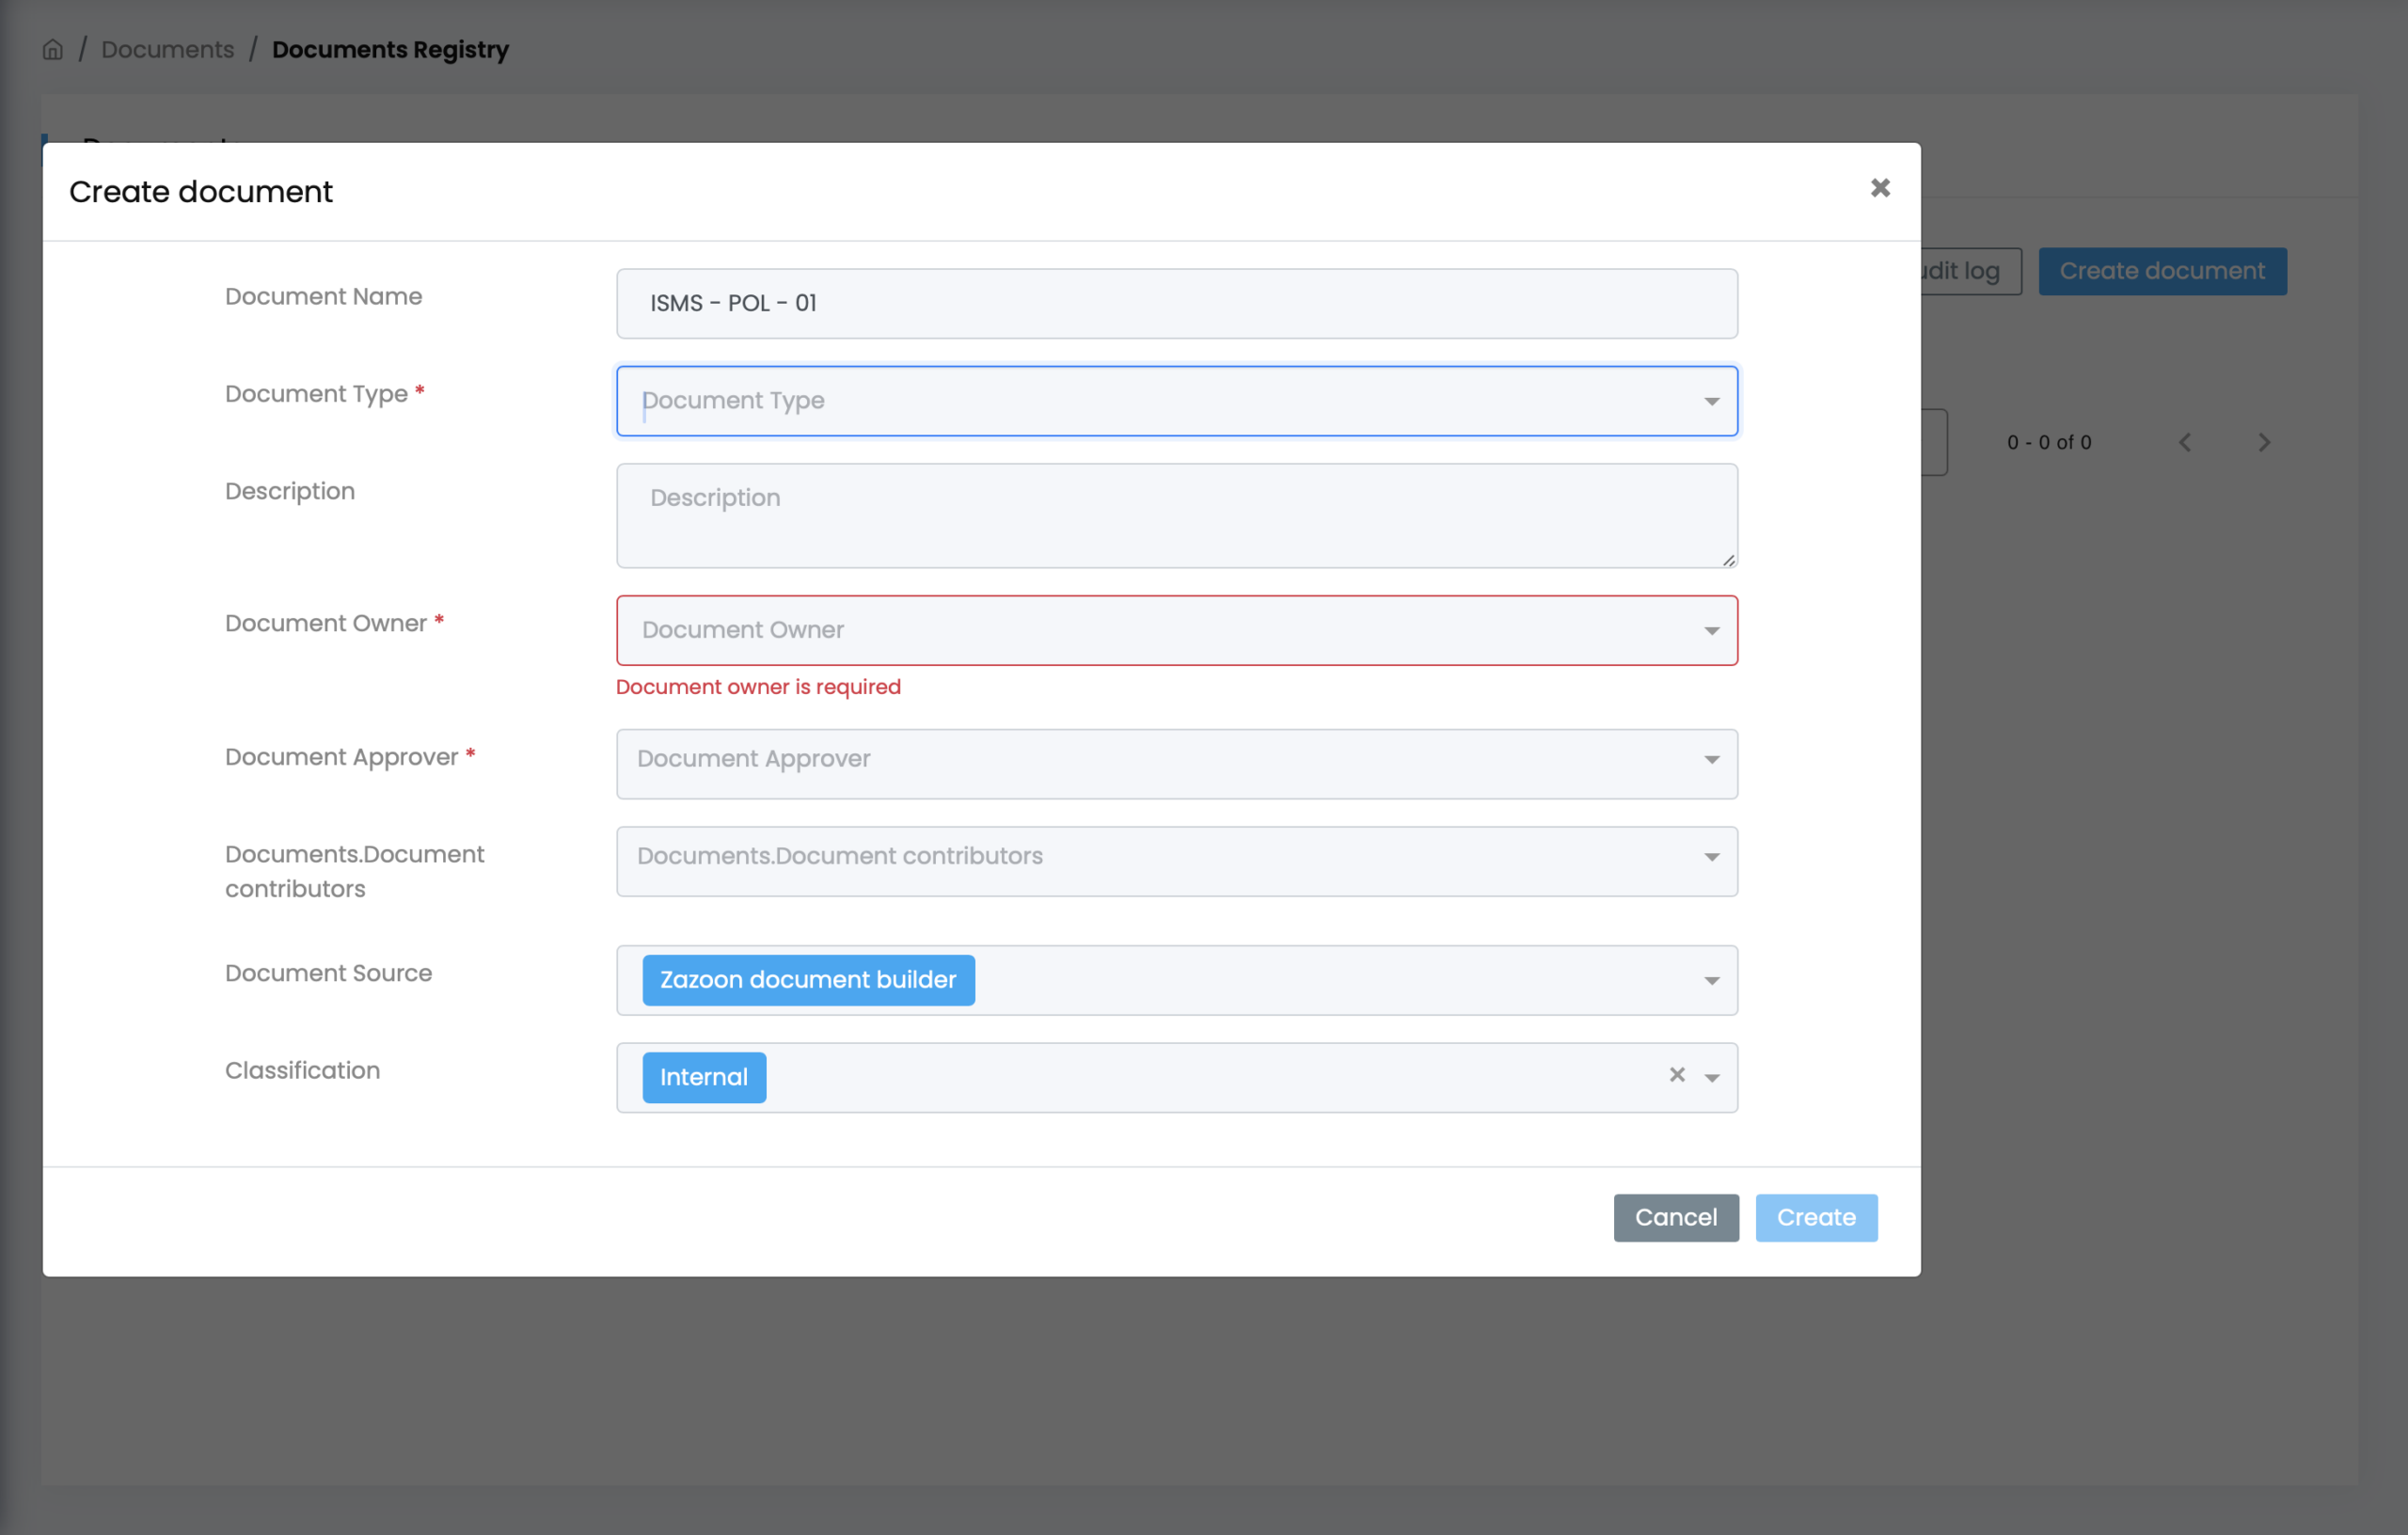
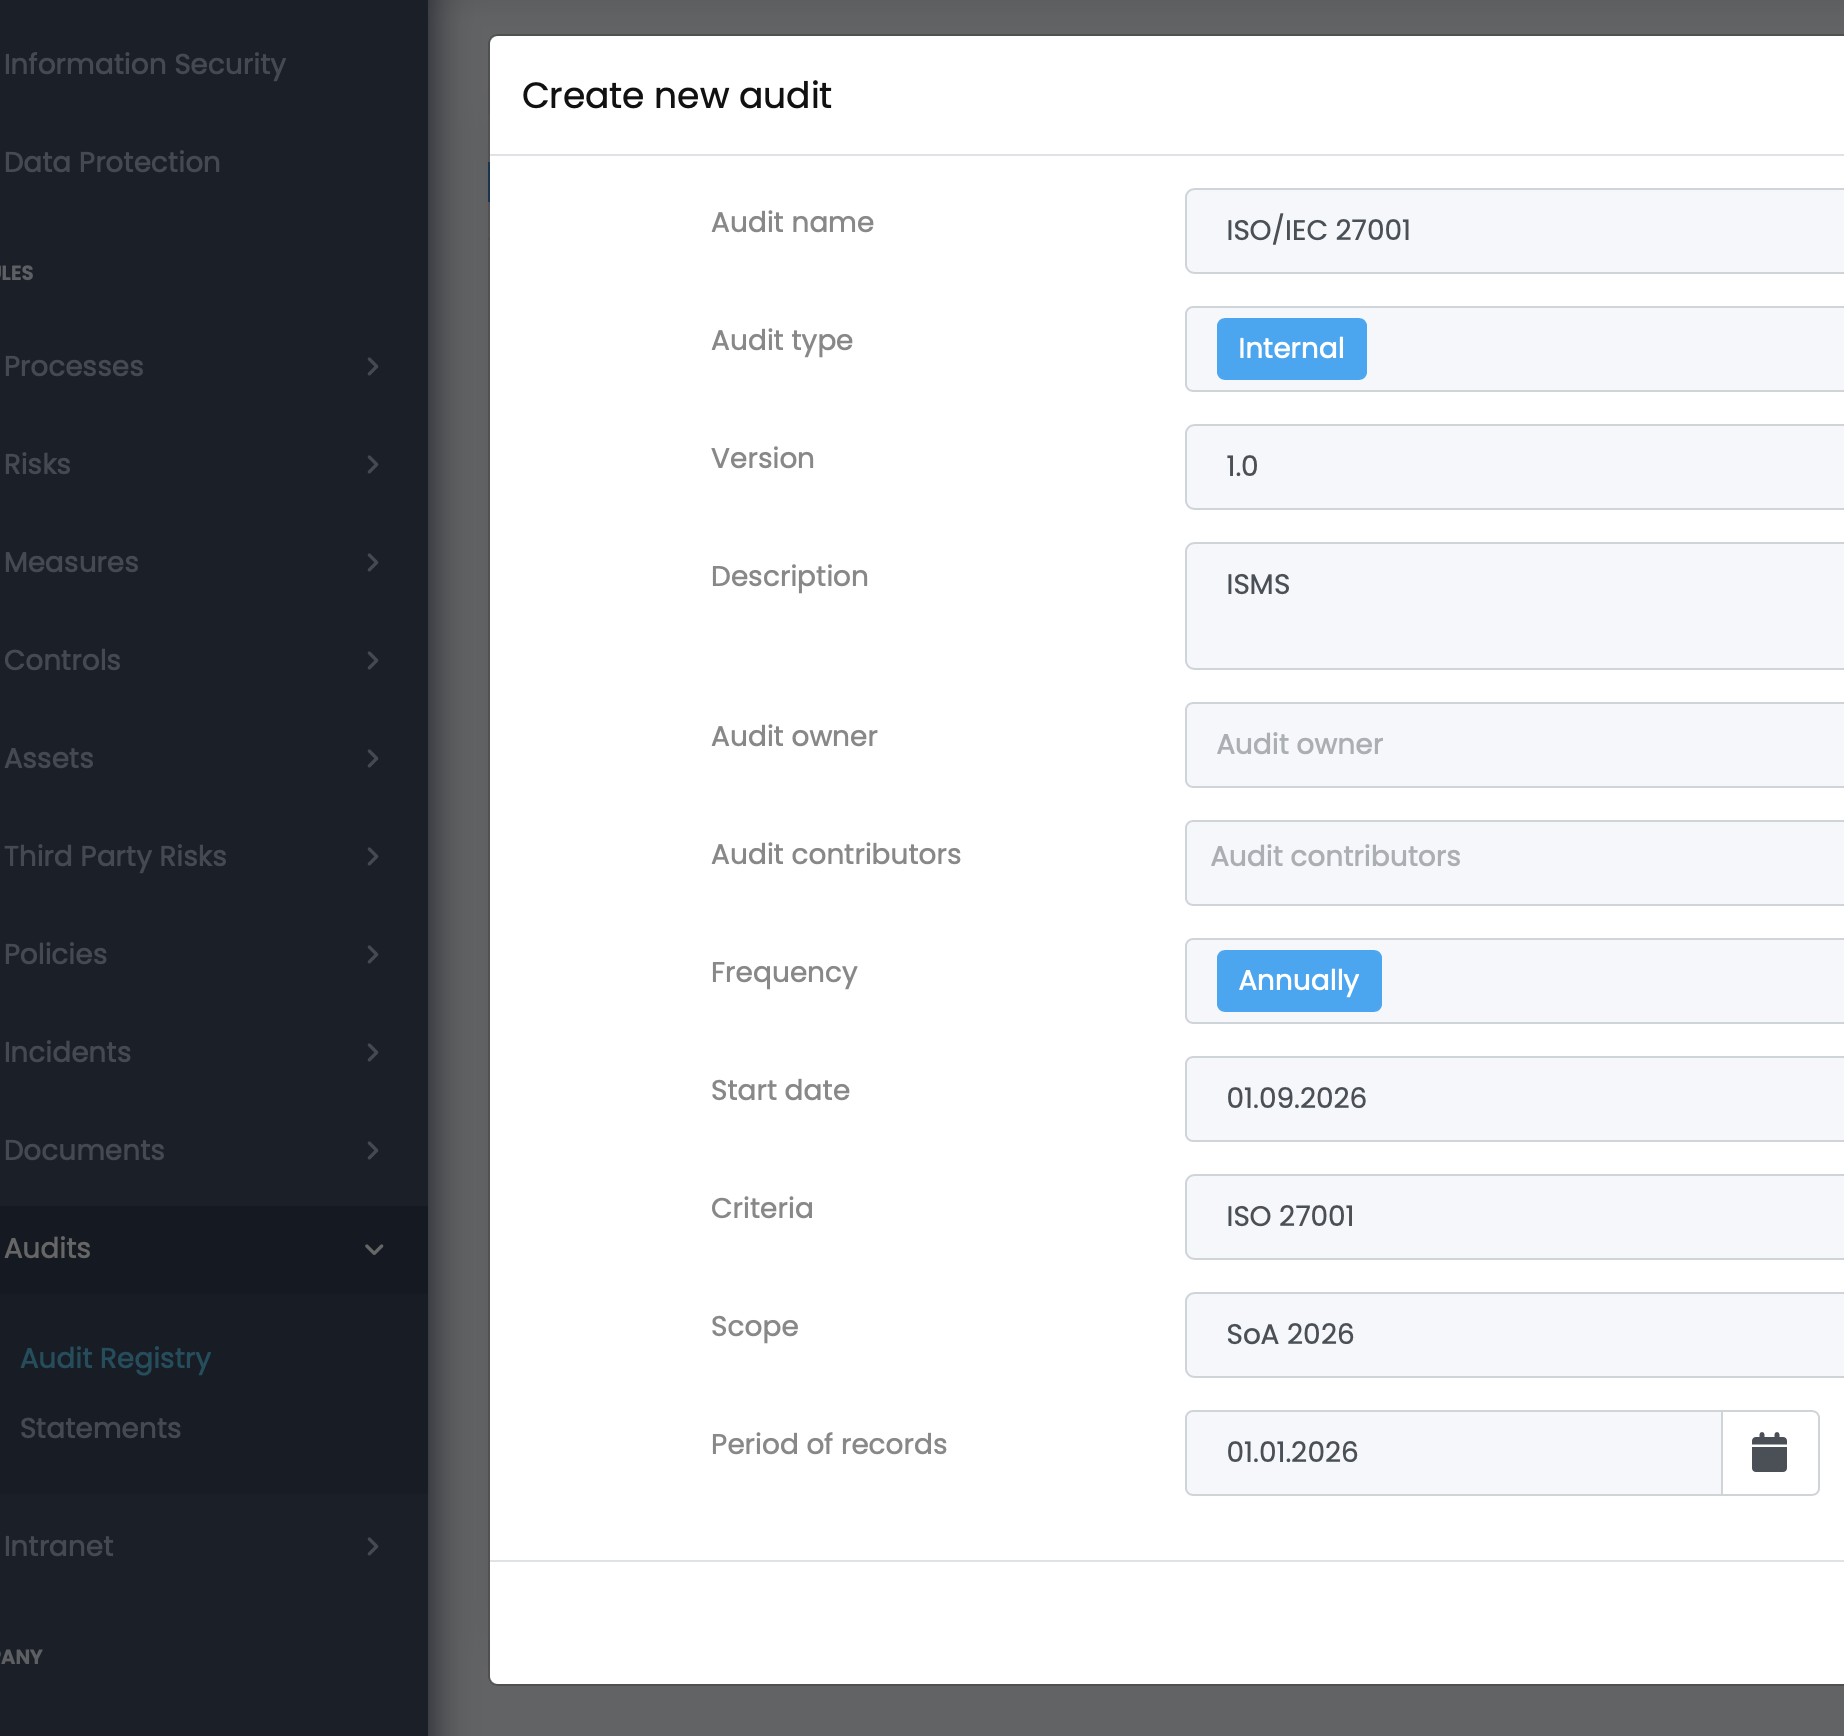
Create and maintain a register of documents such as policies, SOPs, and working or guiding instructions from one centralised register. Map these documents to the controls and the evidence you might need for an ISO/IEC 27001 audit. Gain control over the document life cycle, including document ownership and the review process.